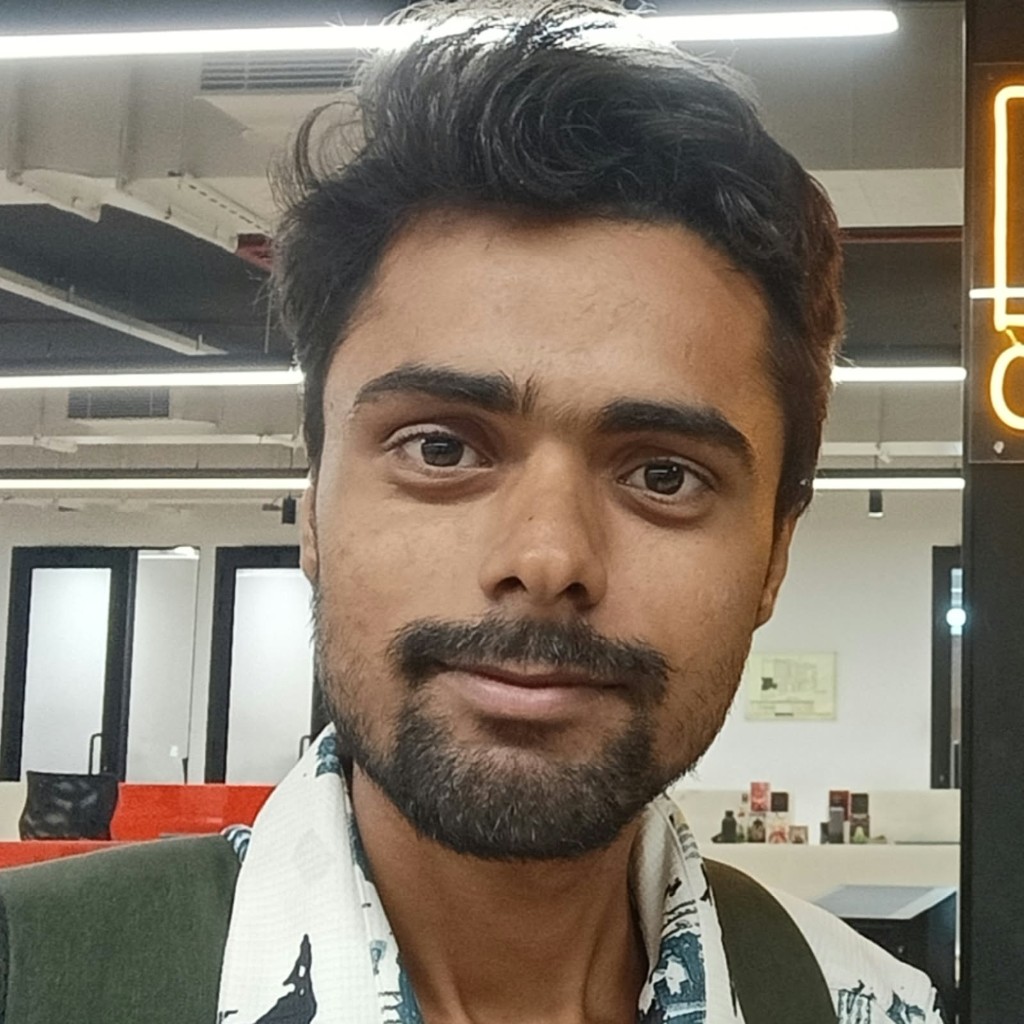
Portrait of Barun Tiwary

Barun Tiwary

Full Stack Engineer · transitioning to Red Teaming ·

Full Stack Engineer moving into red teaming. I’ve built production systems — now I’m learning to break them.

Shipping authentication, APIs, device networks, and deploys showed me where real systems crack. I’m turning that builder’s view into offensive security: web and API exploitation, Linux and network attacks, and lab work written up honestly.

now rad labs · full stack · learning offensive security

Selected work

Security track

Experience

All work

Rad Labs Working

Sep 2026 – Present

Full Stack Engineer / Project Lead: building a healthcare mobile app from the ground up.

  • Lead development of a healthcare mobile application, and extend the existing backend it shares with web dashboards and production workflows.
  • Build production features across React Native / Expo, APIs, authentication, data flows, and backend services without breaking existing consumers.
  • Attack surface: patient data, authentication, and a backend that other clients already depend on.

Consultifi Data

Feb–Jun 2026

Full Stack Engineer: production ERP workflows with device integrations.

  • Built ERP workflows across frontend, backend services, databases, and device integrations with React / Electron, SQLite / PostgreSQL, and REST APIs.
  • QR-based workflows, real-time updates, hardware integrations, and offline-first sync with idempotent writes.
  • Attack surface: device identity, plant-to-plant isolation, and replay through the sync queue.

SIA Health

May–Oct 2025

Full Stack Developer: full-stack features in a healthcare product.

  • Developed and maintained features across frontend interfaces, backend APIs, database workflows, and third-party integrations.
  • Translated requirements into working features and investigated production issues.
  • Attack surface: user input in health-related forms, and how that data is validated and stored.

Autonomous Work

Jan–Mar 2025

Full Stack Developer: web application features across the stack.

  • Built web application features across frontend and backend layers, integrating APIs and database-driven workflows.

Achievements

Open source: Mailchimp integration for Corsair

Merged PR · Jul 2026

Added 56 Mailchimp Marketing API endpoints and 4 webhook triggers to corsairdev/corsair, with OAuth 2.0 and API-key auth, webhook-secret validation, multi-tenant routing, and 56 unit tests.

View PR #351 · Read the security write-up

Principles

Know how it’s built before you break it

Shipping auth flows, APIs, and deploys is how I learned where they get misconfigured.

Every trust boundary is an attack surface

A device token, a webhook URL, and a database port are all doors. Know which ones are open.

Defaults are the real entry points

My own database was breached through a default password, not a clever exploit.

Label what’s real

Shipped, practiced in labs, or learning. Never blurred together.

Writing

All posts